Multi-factor authentication policies are a subset of overall authentication policies.
The first decision choice: which methods are suitable for my company? The two choices available: TOTP (time-based one time password), and WebAuthn.
TOTP will work with a variety of applications (Authy, Google Authenticator, Microsoft Authenticator). No network access is required, it is strictly synced via time and the user typing in a code.
WebAuthn provides a variety of sub-methods:
- Computer Trusted Platform Module (TPM)
- Phone-based push (“was this you?”)
- USB-based FIDO2 devices (e.g. YubiKey)
- PassKey
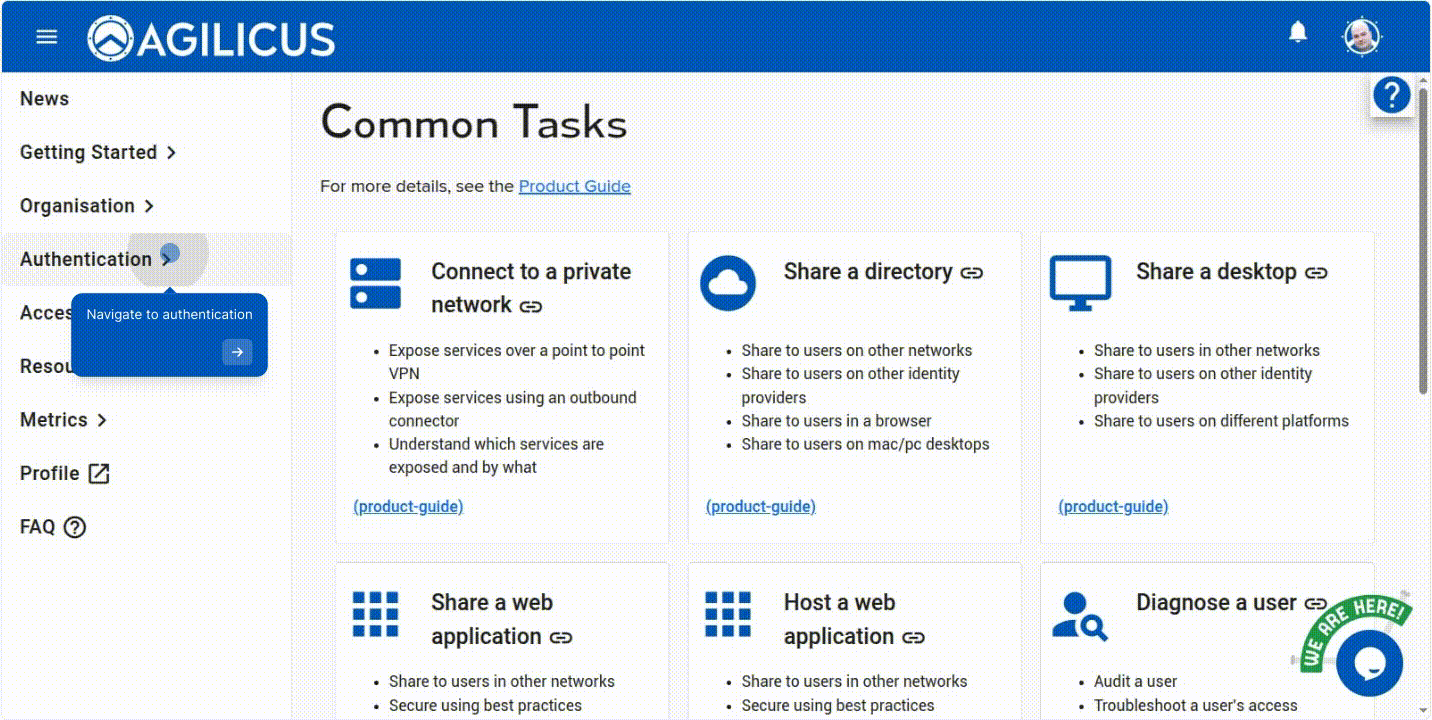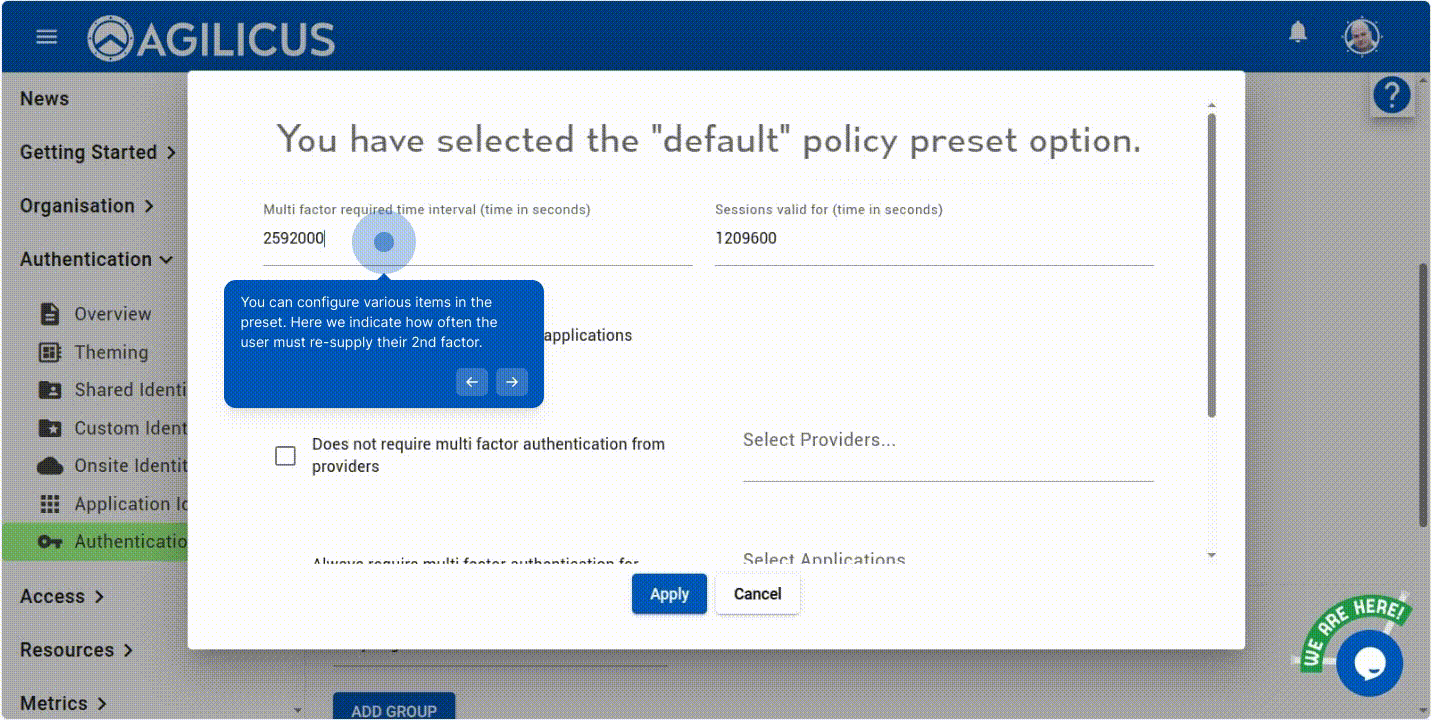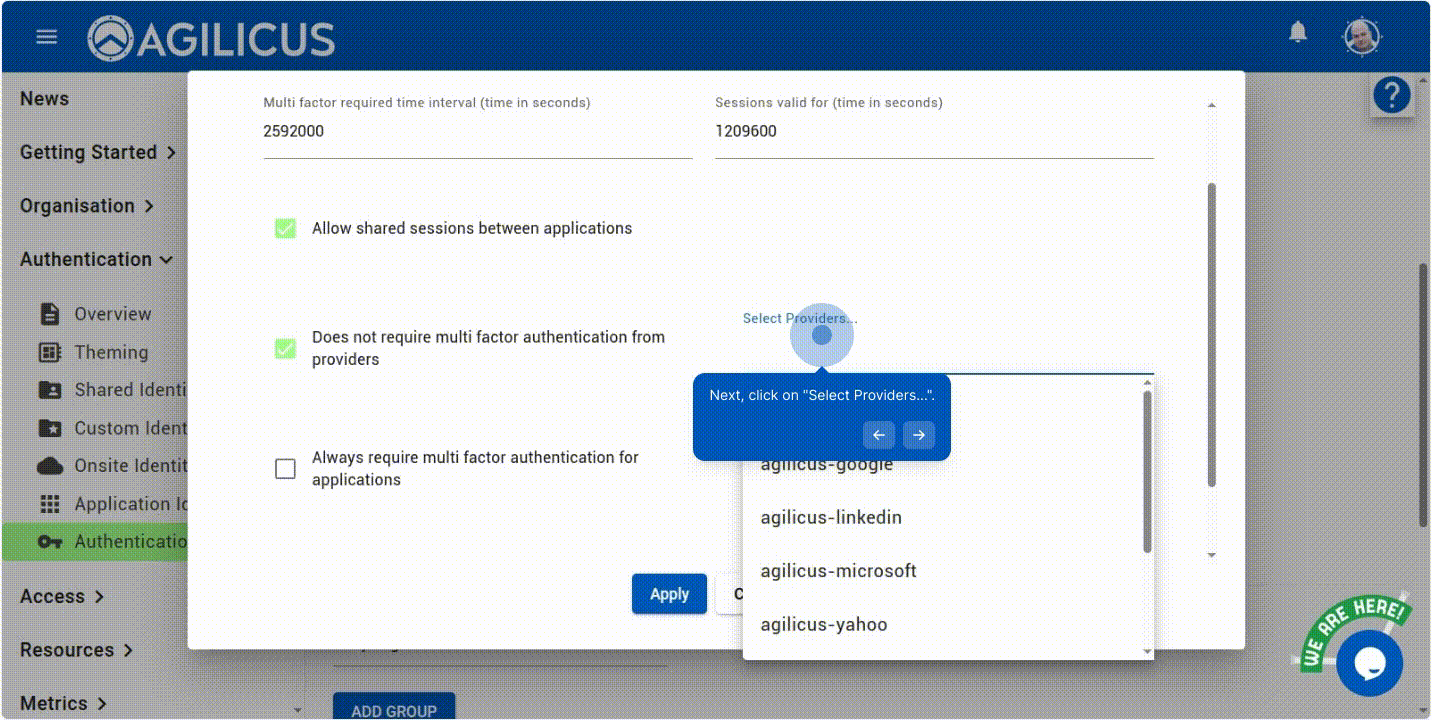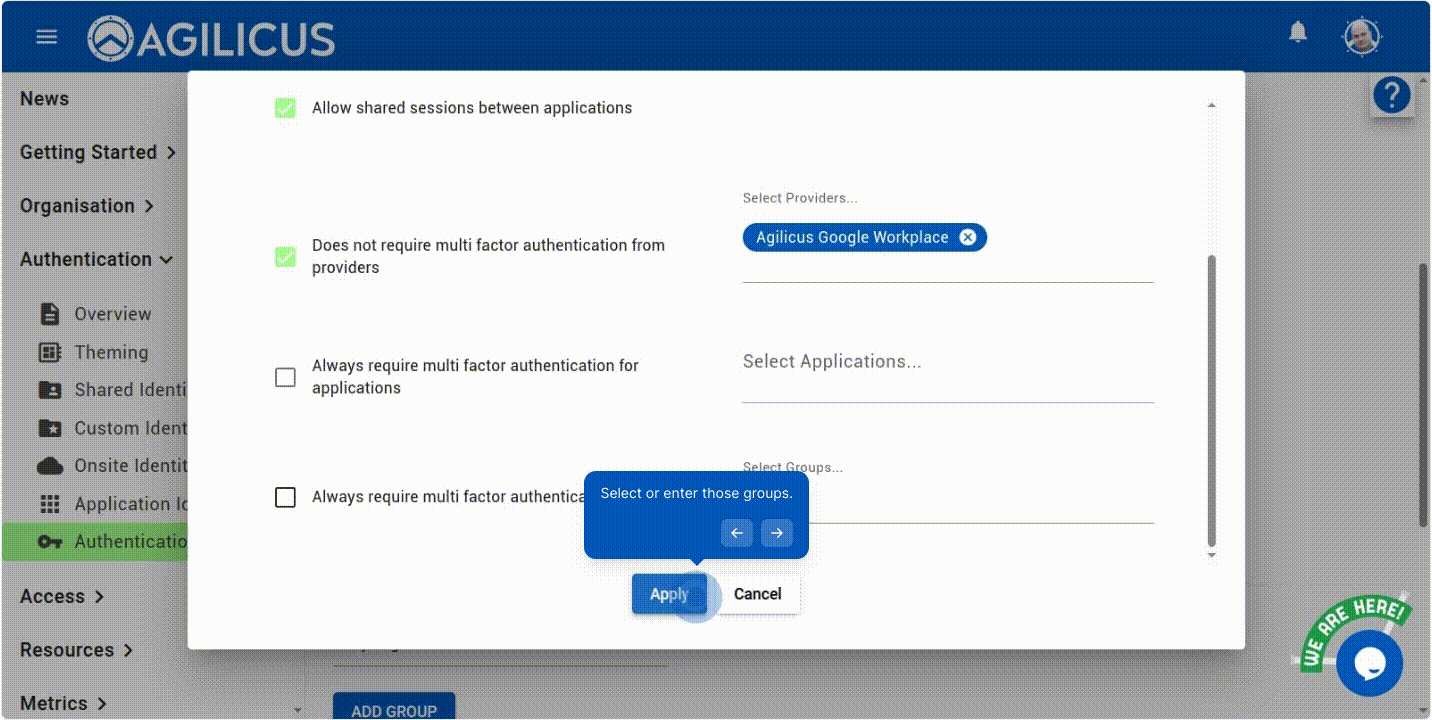
Use a preset authentication policy as a starting point for the majority of the parameters.