End users can setup their multi-factor via https://profile.__MYDOMAIN__. On the ‘profile’ menu, select ‘multifactor authentication’. From here, depending on the administrator setup, they will have one or two methods:
- TOTP (Time-Based One-Time Password).
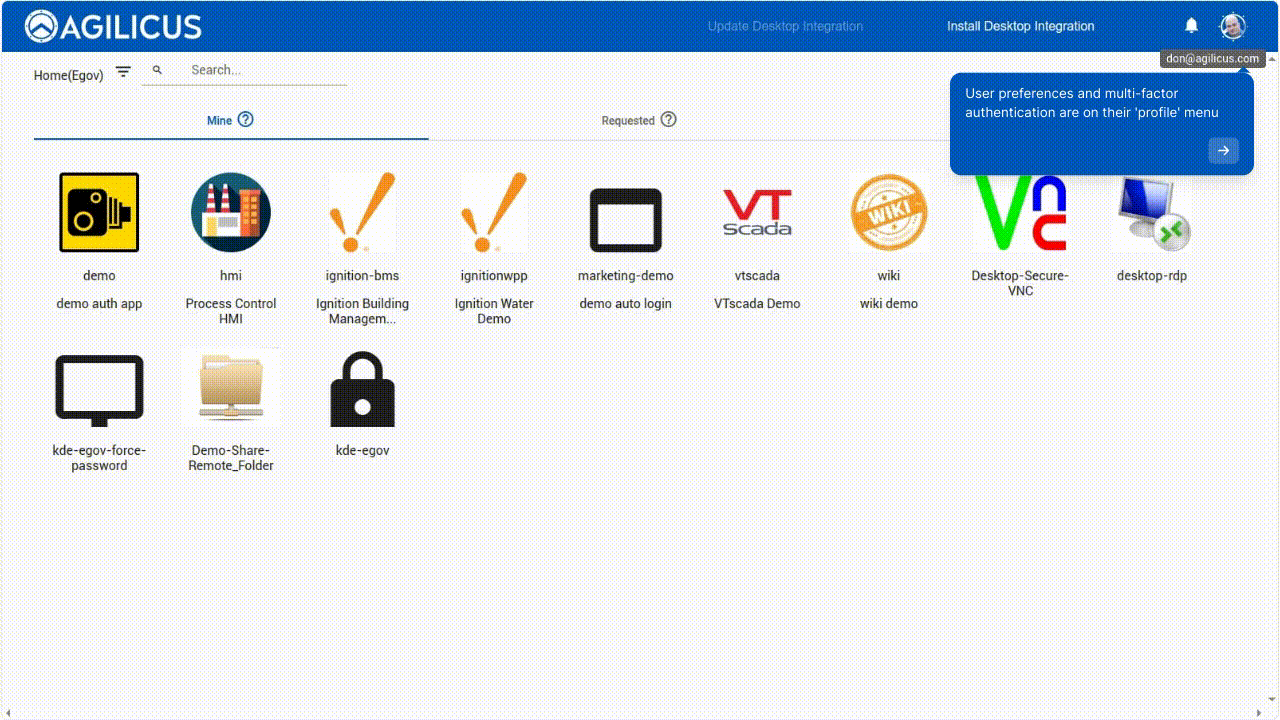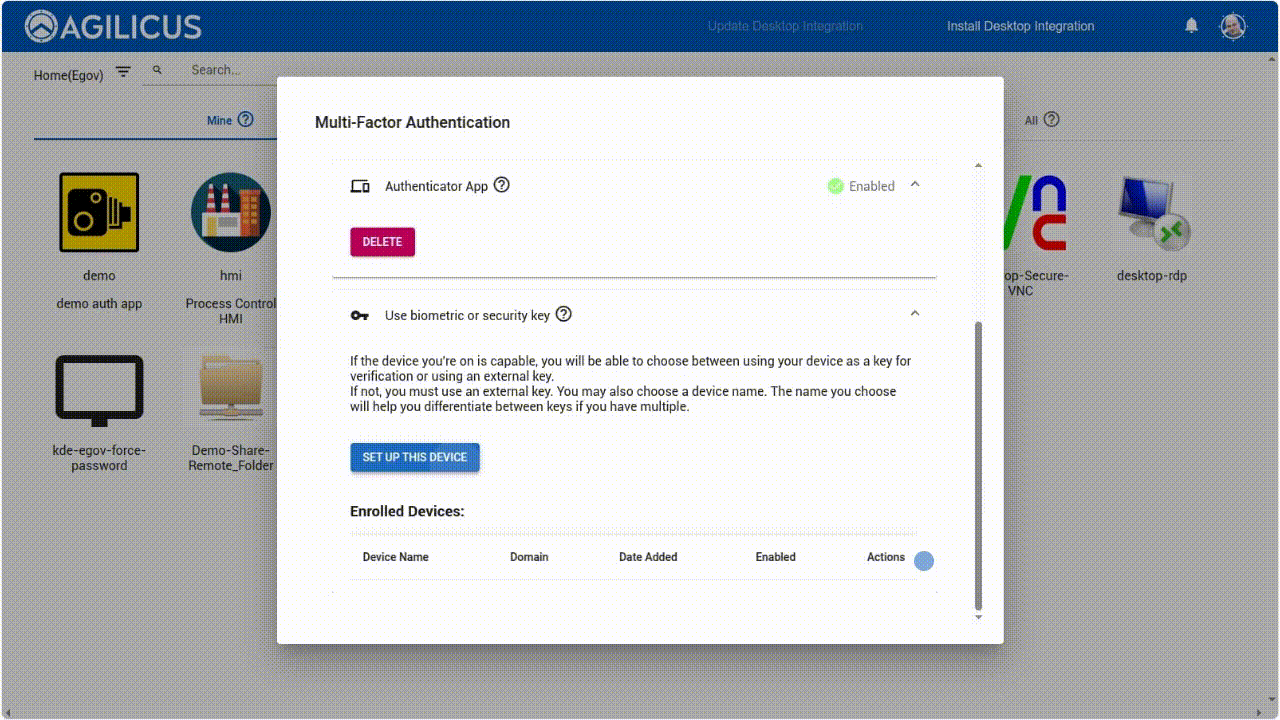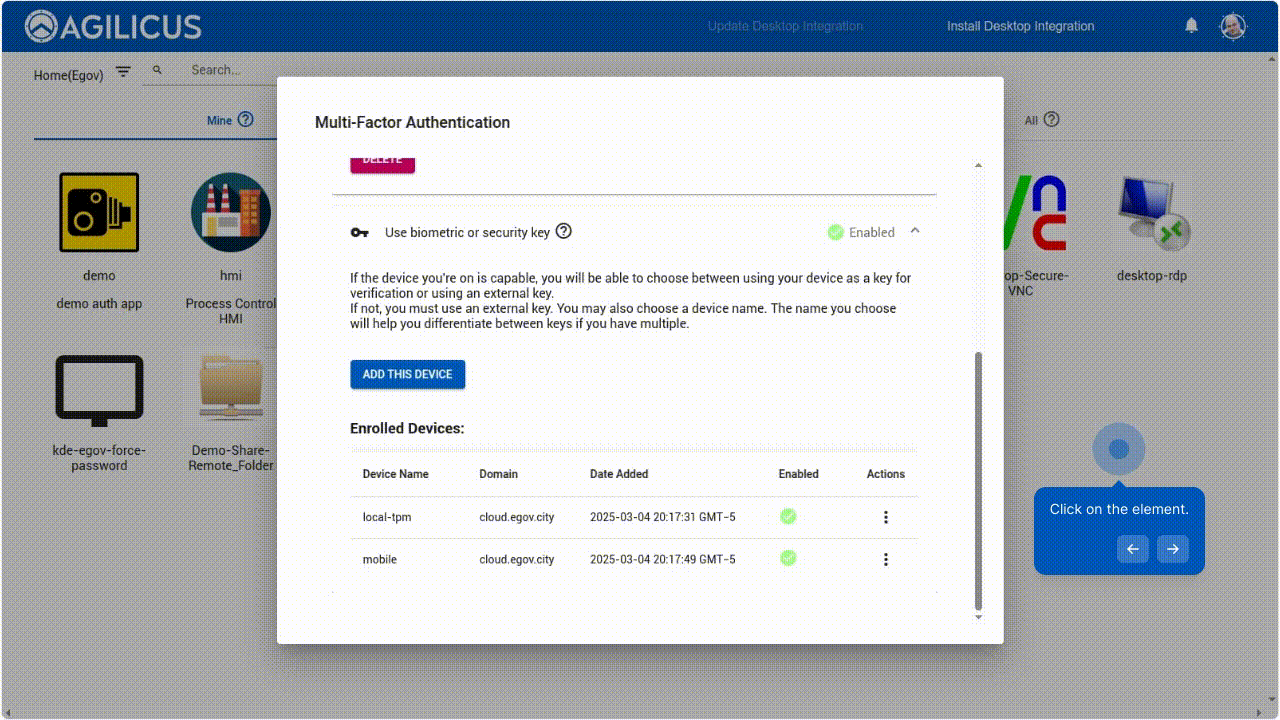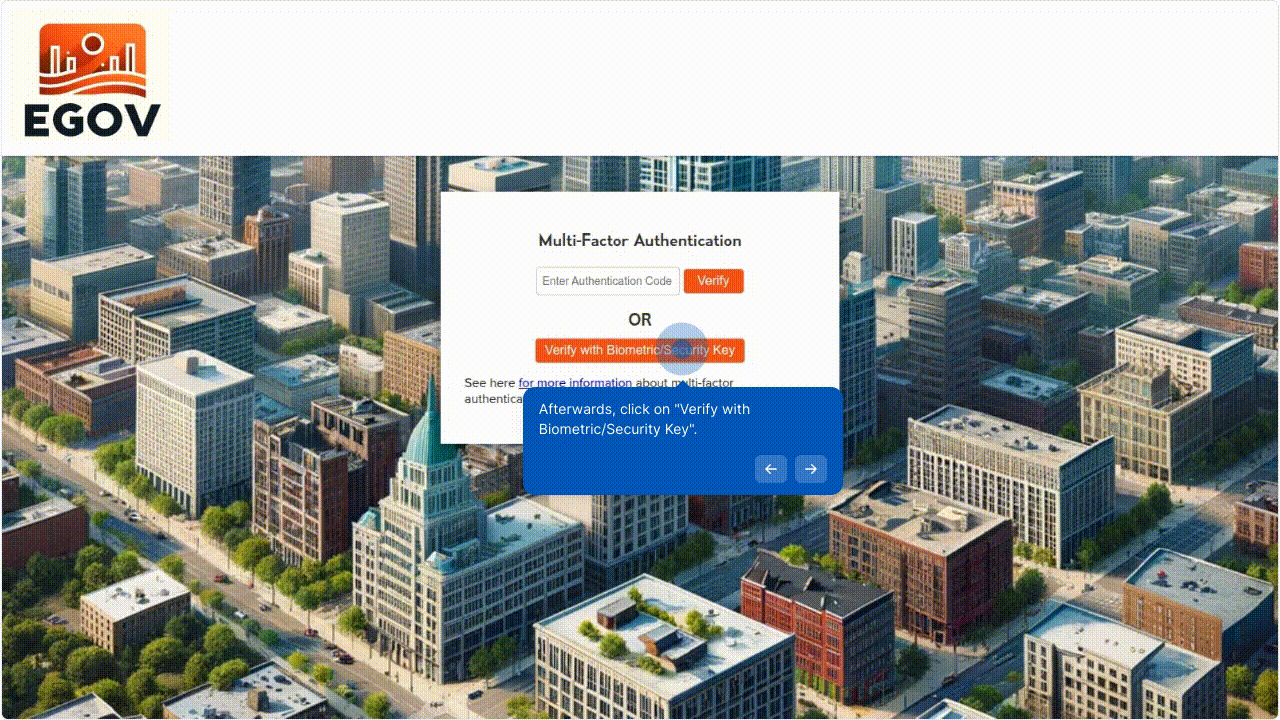
- WebAuthn (USB FIDO keys, Trusted Platform Modules, Biometrics, PassKey)
Both are secure. Both are completely private: no information is exchanged from their device to the system.
The WebAuthn set of standards are typically simpler for end-users to use: they are push-based, they are locked to a single device.
The user can enroll multiple WebAuthn methods (e.g. my phone, my work laptop TPM, my YubiKey).